- Ransomware group The Gentlemen has listed Nvidia on its dark web extortion website, claiming to possess company-related data and threatening to release it.
- Nvidia has not publicly confirmed a security breach, and the hackers have not provided evidence or samples of the allegedly stolen information.
- The Gentlemen has reportedly claimed more than 1,100 victims across 95 countries, although cybersecurity researchers warn that some of its previous claims have been exaggerated or incorrectly attributed.
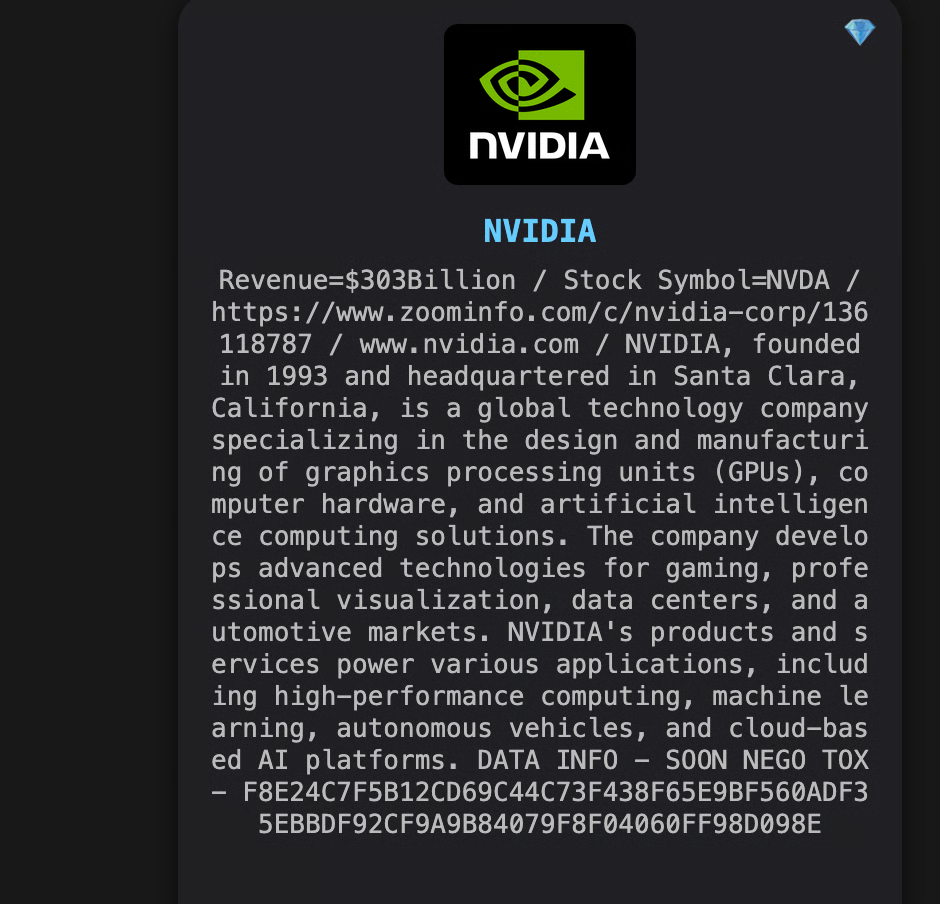
Nvidia has become the latest target of an alleged ransomware extortion attempt after cybercriminal group The Gentlemen added the technology company to its dark web victim list.
According to a report from Cybernews, the group claims to possess Nvidia-related information and is threatening to publish the data unless its demands are addressed.
However, the alleged breach remains unverified, with no publicly available evidence confirming that Nvidia’s systems were compromised.
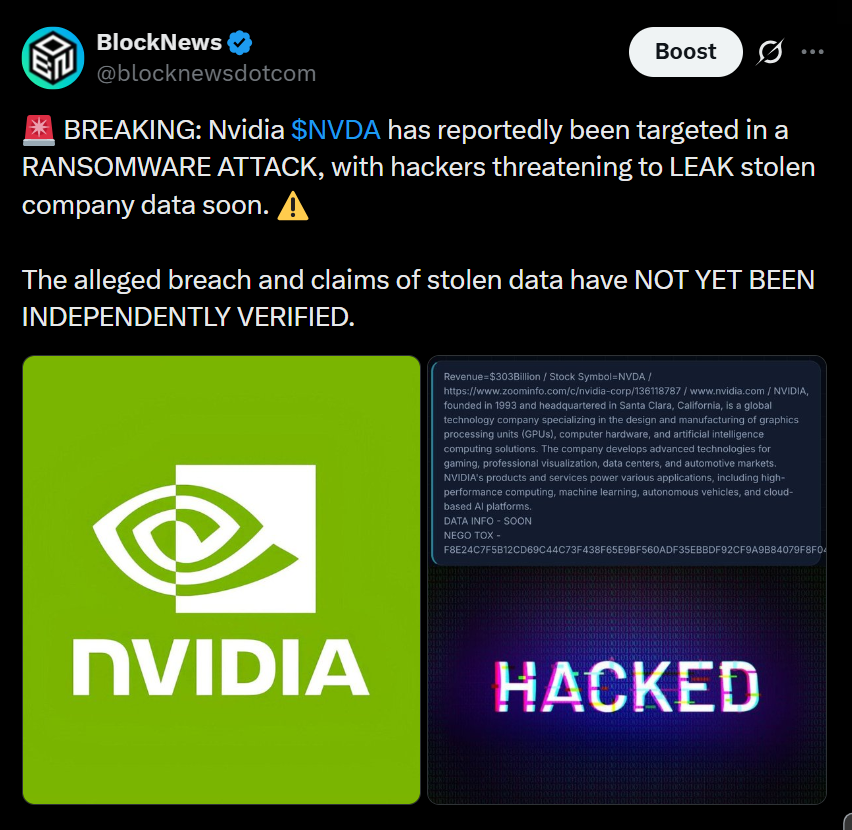
The hackers have not disclosed what information they supposedly obtained, when the alleged attack occurred or which part of Nvidia’s operations may have been affected.
The development comes as Nvidia remains one of the world’s most prominent technology companies, playing a major role in artificial intelligence infrastructure and accelerated computing.
Hackers Threaten to Release Allegedly Stolen Nvidia Data
The Gentlemen published Nvidia’s name on its dark web extortion platform, suggesting that the company could face a potential data leak.
The listing reportedly includes a short description of Nvidia, an encrypted messaging contact for negotiations and a countdown timer.
At the time Cybernews examined the listing, the timer indicated approximately 234 hours before the threatened release.
However, the ransomware group did not publish any samples of the allegedly stolen information.
It also failed to identify the affected business unit or explain how the supposed intrusion occurred.
Nvidia has not publicly confirmed that its systems were breached.
Cybernews said it contacted the company for comment, but no official response was available in the original report.
Without supporting evidence, it remains unclear whether the hackers accessed Nvidia’s internal systems or obtained information from another source.
Cybersecurity experts have warned that ransomware groups sometimes publish company names to increase pressure before providing proof of an intrusion.
Cybersecurity Researchers Question Nvidia Breach Claims
Cybernews researcher Aras Nazarovas urged caution when evaluating the ransomware group’s allegations.
According to Nazarovas, The Gentlemen has previously exaggerated incidents, incorrectly attributed victims and reused stolen information from earlier breaches.
He emphasized that the group has not provided any data samples supporting its latest claim involving Nvidia.
The lack of evidence makes it difficult to determine whether sensitive information was exposed or whether the incident represents a legitimate security breach.
Nazarovas suggested that the listing could involve incorrectly attributed information or a relatively limited incident.
However, that assessment remains preliminary, and the actual circumstances cannot be established without additional evidence.
The situation highlights an important distinction between a ransomware group’s public claim and a confirmed cybersecurity incident.
Although the appearance of a company’s name on an extortion website can raise concerns, it does not independently establish that its systems were compromised.
For Nvidia, confirmation would require additional technical evidence, credible leaked data or an official disclosure from the company.
The Gentlemen Ransomware Group Expands Global Operations
The Gentlemen emerged around July 2025 and quickly developed into one of the more active ransomware-as-a-service operations.
According to ransomware tracking platform Ransomware.live, the group has claimed approximately 1,123 victims across 95 countries.
The operation reportedly offers affiliates a 90% share of ransom payments, creating financial incentives for cybercriminals to participate in attacks.
Cybersecurity researchers have also linked the group to the use of artificial intelligence for developing ransomware tools and supporting post-compromise activities.
A Barracuda report indicated that The Gentlemen evolved from an earlier affiliate operation known as ArmCorp, which previously operated within the Qilin ransomware ecosystem.
The group reportedly communicates in Russian, recruits through Russian-speaking cybercrime forums and generally avoids targeting organizations in Commonwealth of Independent States countries.
However, researchers have not established evidence of collaboration with a nation-state.
Organizations previously named in incidents involving the group include NATO contractor Indra, European data transfer platform FTAPI, LA Metro, Glassdoor and MoneyGram.
The group’s history demonstrates its ability to attract attention through high-profile extortion claims, although individual allegations require independent verification.
For Nvidia, the immediate concern is whether the hackers can produce credible evidence supporting their claims.
Until the company confirms an incident or verifiable information emerges, the alleged ransomware attack should be treated as an unconfirmed claim rather than an established data breach.
The coming days could provide further clarity as the group’s publication deadline approaches and cybersecurity researchers continue examining the listing.